Premia Labs Loses $464K in Arbitrum Vault Exploit
Premia Labs, the firm behind Kyan, lost an estimated $464,600 from its Arbitrum options vaults on November 1. PeckShield traced the funds through Chainflip and NEAR Intents into Bitcoin, and no reimbursement plan has been published yet.
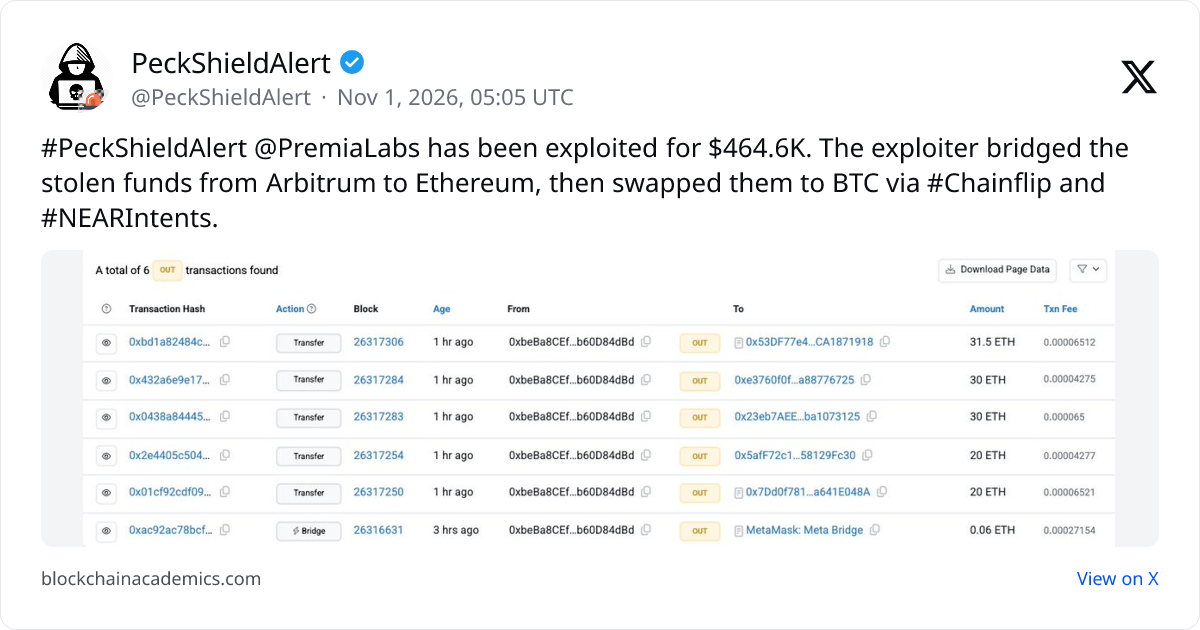
An attacker drained an estimated $464,600 from Premia Labs options vaults on Arbitrum on November 1, and the loot was converted to Bitcoin within hours. Premia Labs is the on-chain development company behind the Kyan derivatives platform. PeckShield traced the stolen funds through Chainflip and NEAR Intents into BTC.
Blockaid flagged the exploit first. In a post on X, the security firm reported about $400,500 drained across two transactions while the attack was still ongoing.
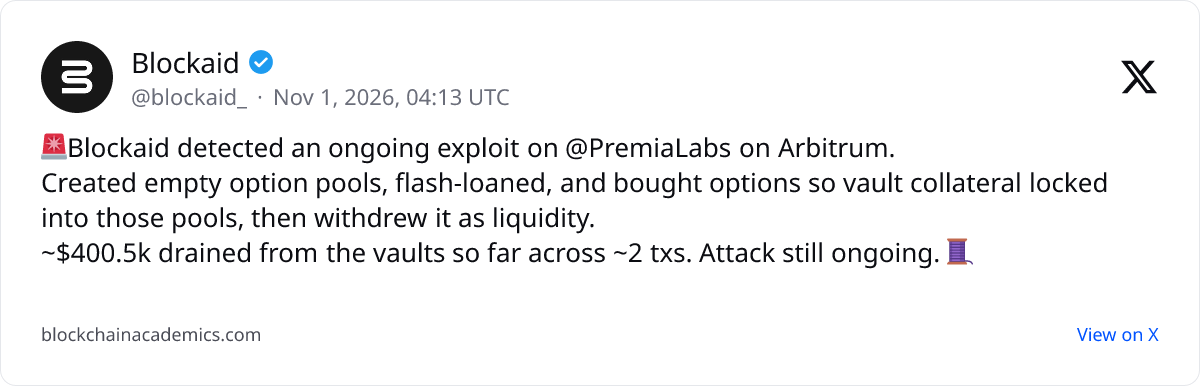
PeckShield later put the figure at $464,600 in its own alert, roughly 131 ETH at the valuation cited in the initial reports. The two numbers are different snapshots of one incident, not separate thefts.
How the attack worked
Per Blockaid, the attacker created empty options pools, borrowed through flash loans (uncollateralized loans that must be repaid within a single transaction) and bought options that locked vault collateral inside those pools. Then they pulled that collateral out as liquidity into wallets they controlled.
The two principal withdrawals landed around 03:15 UTC, roughly one second apart, according to transaction records. Independent on-chain analysis identified six affected vaults. The drained assets: 3.64 WBTC, about 43.47 WETH, 48,479 USDC.e and 46,215 ARB.
The laundering trail
PeckShield tracked the funds from Arbitrum to Ethereum, then through Chainflip and NEAR Intents, both cross-chain swap platforms, into BTC. Routes like this limit traceability and make freezes harder, which is exactly why exploiters keep using them.
Be careful with the inference, though. The transfers do not establish that Chainflip or NEAR Intents knowingly helped the attacker, and neither has been identified as the source of the vulnerability.
As of the initial security reports, Premia Labs had not published a detailed explanation, recovery arrangements or a reimbursement plan. If you hold positions in the affected vaults, that silence is the risk to watch until the team says more.
Context
At under $500K, this is small change next to the Binance incident of October 29, which the reports tie to a wider run of attacks. The FBI has called on DeFi operators to help freeze stolen funds, and one estimate puts 2026 hack losses at a record $8.73B, with North Korea-linked actors behind nearly 90%. TRM Labs puts that share at 76%. The two figures have not been reconciled, and nothing in the reports attributes the Premia exploit to any group.
The weakness Blockaid described sits in Premia's vault and pool design, and nothing in the reports points at Arbitrum itself. Network activity is no shield against bad contract logic, even on a chain where Arbitrum One daily active addresses hit 571,767 in October.