Claude Writes Linux Exploit for Bug Ubuntu Has Not Patched
Anthropic says Claude wrote a working remote root exploit for CVE-2026-98432, a 9.8-severity Linux flaw present since kernel 4.4. Red Hat, Debian, SUSE and others have shipped fixes, but Ubuntu still lists every release from 16.04 to 26.10 as vulnerable with no fix date.
A stranger can take full control of a Linux server over the internet, with no password, using an attack that Anthropic says its Claude model wrote. The flaw behind it, CVE-2026-98432, has been present since Linux version 4.4 and scores 9.8 out of 10 for severity. Ubuntu's tracker still lists every release from 16.04 to 26.10 as vulnerable.
Anthropic described the attack on Oct. 27 in a research post covering five targets: Chrome, Safari, Android, Windows and Linux. Claude wrote the Linux exploit after initial prompting, using an unreleased internal model. Finding a hidden spot in memory takes under an hour, and running a command as root takes five more minutes. Anthropic has also written that its researchers could take over certain Linux machines within 53 minutes.
How the flaw works
The bug is a race condition: one part of the system discards information while another still uses it. Anthropic said the property that makes it practical is that failure is cheap.
"An enabling property of this race condition is that a lost race only fails the handshake without crashing the whole system"
Anthropic
An attacker can therefore retry indefinitely. Anthropic's version of the attack needs a server exposing a multipath TCP (MPTCP) listener, and Go programs have enabled MPTCP by default since Go 1.24. The Go Security Team cautions against reading that requirement as a limit:
"While the demonstrated exploit requires the target system to expose an MPTCP listener, the underlying bug is not specific to MPTCP"
Go Security Team
It recommends upgrading to a patched kernel.
Patch status
Red Hat released fixes for RHEL 8, 9 and 10 on Sunday, Nov. 1, including RHSA-2026:93412. Debian, SUSE, Oracle Linux and Amazon Linux have shipped fixes, at least for some versions. Red Hat's security bulletin also offers a temporary firewall rule, which it says "reduces exposure to this vulnerability but cannot fully prevent it." A full working solution is still under development.
Ubuntu trails its peers. Fixes are in progress for 22.04, 24.04, 26.04 and 26.10, but no release date is given. Versions 20.04, 18.04 and 16.04 show only "Vulnerable."
Reaction
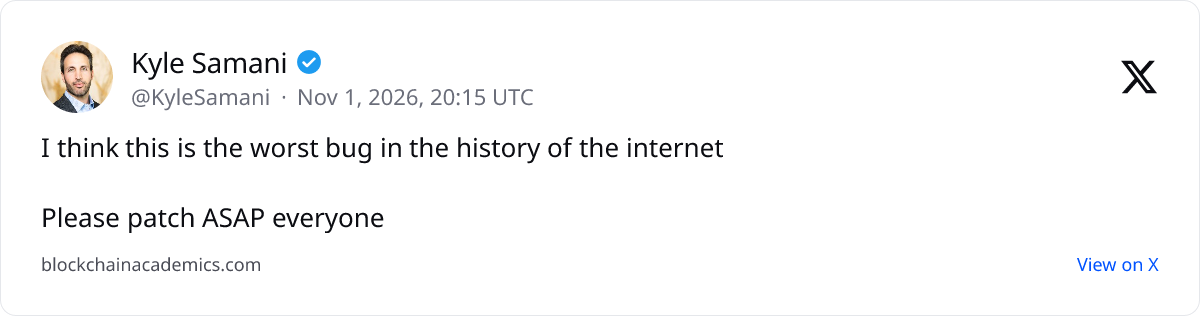
Over the weekend the bug acquired a loud public profile. Shopify's CEO drew three million views on Saturday with a post on X about the flaw.
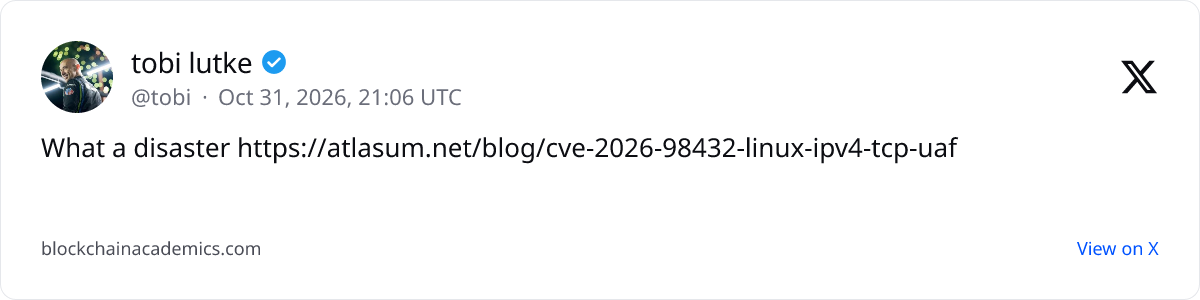
"This is the worst bug in the history of the internet," Kyle Samani wrote, and ex-Coinbase engineer Mert Mumtaz wrote that it is worse than that. An Anthropic staff member put it more plainly: "I can't think of a more severe bug."
The framing is contested. Some accounts describe the bug as "zero-click" and say Claude's work turned a relatively niche error into an easy-to-exploit flaw; the exploit Anthropic demonstrated, however, depends on an exposed MPTCP listener. As of Monday, Amazon was still upgrading its infrastructure, and Anthropic was helping companies apply patches and urging partners such as Ubuntu to fix their code.
What it means
The episode shows AI moving from bug discovery to working exploit development. Anthropic's earlier Claude Mythos model helped Mozilla find 271 bugs in Firefox. Defenders are already feeling the volume: Firedancer now charges 1 SOL per bug report after a contest drew 809 reports but only 127 unique findings. For operators of Linux servers, including node and validator infrastructure, the practical step is to check kernel versions and MPTCP exposure now, since an unpatched Ubuntu fleet has no vendor fix date to wait on.