Luxor Commander Hijack Redirected Bitcoin Hashrate to OCEAN Pool
Attackers compromised Luxor's Commander fleet-management tool and pointed customer Bitcoin hashrate at the OCEAN pool. Luxor patched it within two hours, pledged full compensation, and its CEO blamed an unspecified AI-enabled attack vector.
Attackers who compromised Commander, Luxor's fleet-management platform, used it to redirect Bitcoin hashrate from just over a dozen customer accounts to the OCEAN mining pool. The intrusion began at approximately 6:00 PM PDT on November 14, and Luxor confirmed the breach on November 15, 2026.
Miners use Commander to monitor and configure their machines. Peak diverted hashrate has been estimated at around 13 EH/s, roughly 1.4% of the Bitcoin network. Initial reports also pointed to about 64,000 machines redirected on Saturday. Luxor has confirmed neither the machine count nor the 13 EH/s figure.
Containment and payout
Luxor patched Commander within two hours of detecting the unauthorized changes and began restoring affected machines to their original pool settings. The company said the problem stayed inside one product:
"We have explored the issue extensively, and it was isolated to the Commander tool. None of Luxor's other services (including Luxor Pool and LuxOS) were affected."
Luxor
No data was exfiltrated, according to reporting on the incident. Luxor has pledged full compensation to affected customers and a post-mortem.
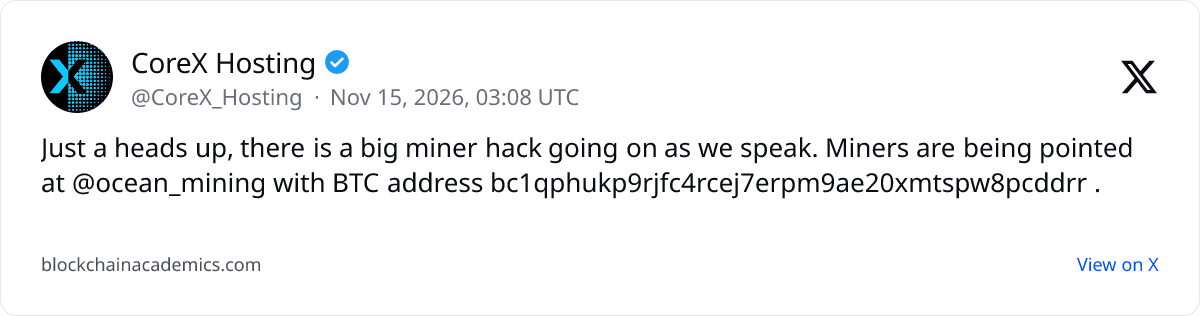
The attackers' take appears small. A Bitcoin address that CoreX identified as linked to the incident received two OCEAN payouts totaling about 0.162 BTC, roughly $10,500. Early reports had suggested the attackers earned nothing.
The AI claim
CEO Nick Hansen said in an X post on Sunday that the attack came through a "sophisticated AI-enabled vector." He has not specified how AI was used. He framed the threat broadly:
"At this moment, anyone running any sort of substantial business, especially in crypto, is inundated with AI-enabled attacks."
Nick Hansen, CEO of Luxor
Hansen also said, "Abliterated models are running 24/7 against your entire surface, looking for a little crack, which they then use to (almost instantly) expand."
Luxor has put most feature work on hold to harden security, Hansen said, and has acquired its own GPUs to run unrestricted open-weight models for defense.
What it means
Luxor's account follows other reported AI-assisted intrusions. Earlier this month, India's cybersecurity agency warned that a group called Crafty Falcon was using AI-powered tools against financial firms, including crypto exchanges. Chainalysis disclosed in October that an attacker used "offensive agentic techniques" to reach its systems, exposing password hashes, live tokens and other customer information.
For Bitcoin itself, the risk looks limited. The diverted share is far from enough to threaten consensus, and the breach was fairly contained, with a modest haul. The open question for miners is operational. Software that can repoint a fleet's hashrate concentrates risk in one place, and the post-mortem Luxor has promised is the next document to watch for how the attackers got in.