Ledger Warns Berlin Buyers of Tampered Wallets, Probes Dubai
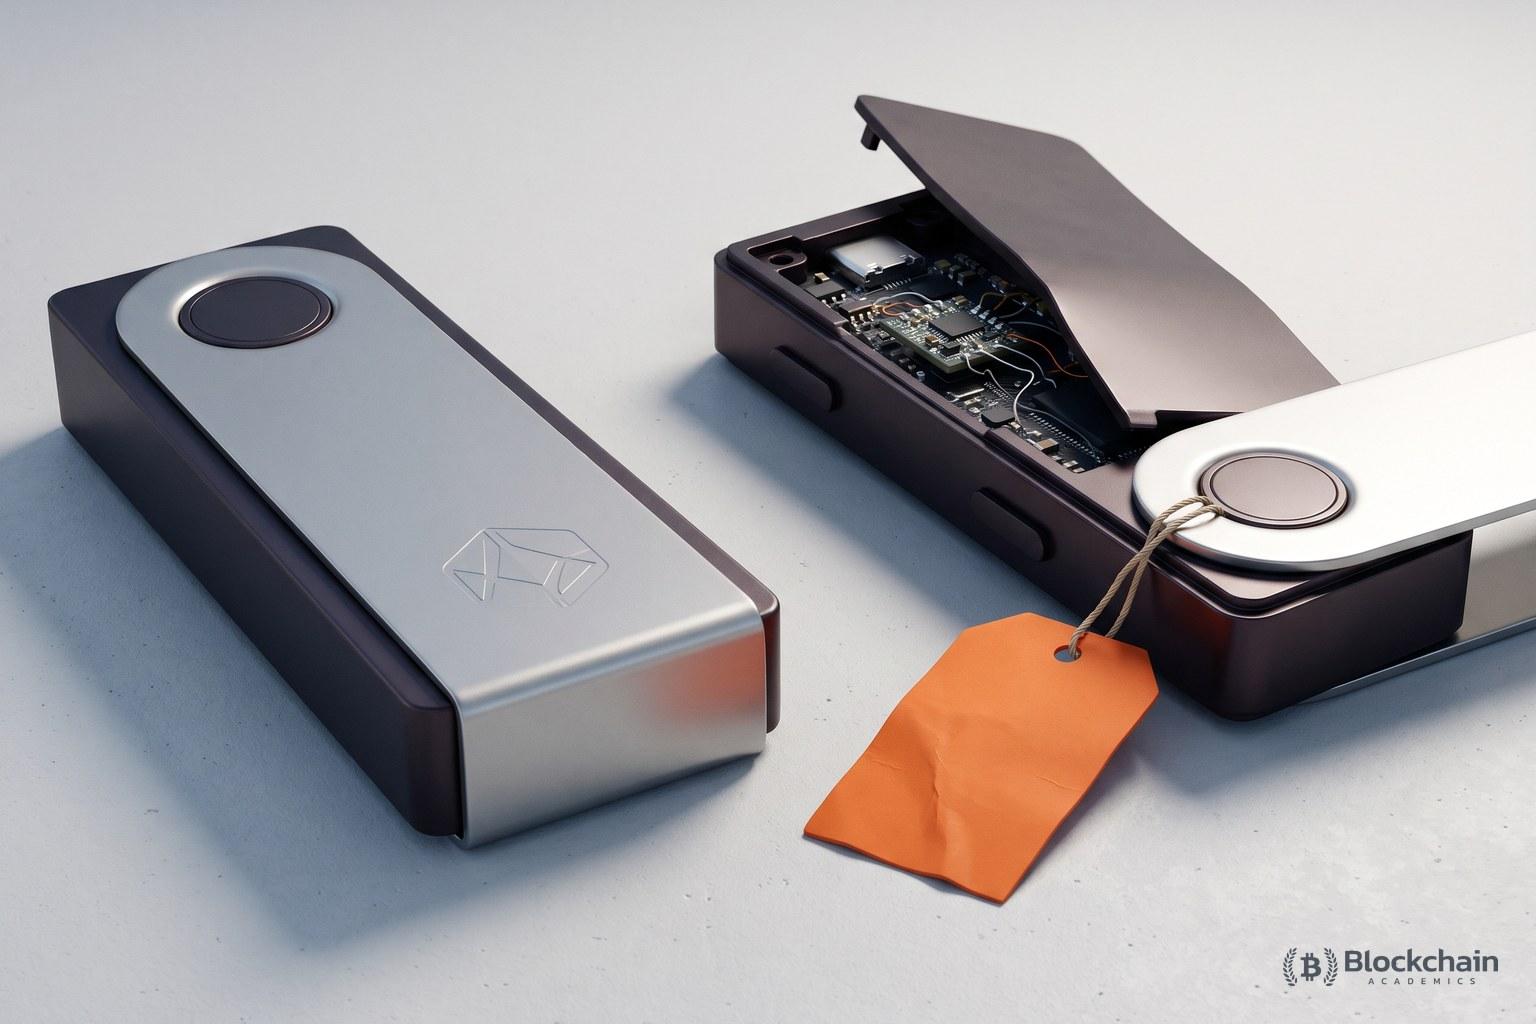
Ledger told Berlin buyers since January 2026 to contact support after finding suspicious devices, and is probing Dubai reports where two users lost $604,000. Ledger says its chip is not at fault. The tampering came through resellers.
Bought a Ledger in Berlin this year? The company wants to hear from you. In a Wednesday update on Nov. 18, Ledger told anyone who bought one of its hardware wallets in Berlin since January 2026 to contact its support team, after its investigation into a tampering campaign turned up several suspicious devices in the city.
Berlin is not the only hot spot. Ledger also acknowledged reports of tampered devices in Dubai, where two customers recently said they lost a combined $604,000 in crypto. The company is investigating reports across Germany and the United Arab Emirates.
Same campaign, new regions
Ledger tied the incidents to the distribution-channel tampering campaign it first investigated in Southeast Asia in October. Back then it asked authorized reseller CryptoBilis to suspend sales and shipments amid reports of crypto thefts. Ledger also confirmed that one Ledger Nano Gen 5 had been affected in the region.
All confirmed tampered devices carried similar physical modifications designed to capture recovery phrases during setup.
That is the ugly part. A recovery phrase is the whole key to the wallet, so once it is captured at setup, the secure chip never gets a chance to matter.
What Ledger says is not broken
Ledger said it found no vulnerability in its secure chip or operating system, and no confirmed cases involving devices bought directly from its website. On Ledger's account, the problem sits in the distribution channel, not the hardware design.
For customers who are worried, Ledger is offering physical inspections, including X-ray analysis, at its factory in Vierzon, France.
In the UAE, Ledger's reseller directory lists Virgin Megastores' Ledger sales as temporarily paused. Investigator ZachXBT, meanwhile, is pressing the company over compensation.
What it means for buyers
The takeaway is blunt: where you buy matters as much as what you buy. Every confirmed case so far traces back to the reseller channel. Buying direct has avoided the problem to date, though Ledger's statement covers only confirmed cases.
The brand's name was already in the security headlines this week. We reported earlier this week that malicious JavaScript served through Optimizely hit 178 sites, Ledger among them. That is a separate incident from the hardware tampering.
If you bought a device in Berlin since January, contact Ledger support. If you picked one up from a third-party seller in Dubai, treat it as suspect until it has been inspected. Never use a recovery phrase that came pre-written, and never reuse one from a device you now doubt.