Cloudflare CEO Reports Millions of Exploit Attempts on Critical PHP Flaws
Cloudflare recorded millions of exploit attempts against two critical PHP vulnerabilities after disclosure, and thousands in the 10 hours before, CEO Matthew Prince said. PHP shipped emergency fixes on Wednesday as the FBI urged organizations to patch or go offline.
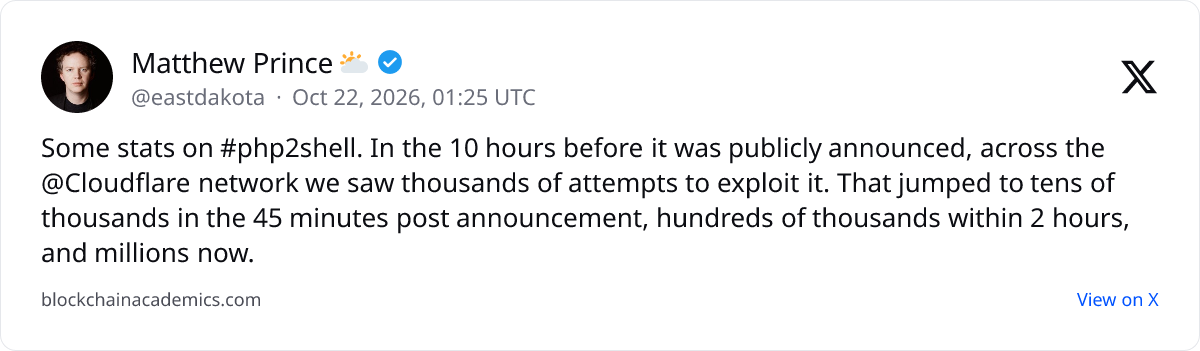
Cloudflare has recorded millions of exploit attempts against two critical PHP vulnerabilities since their disclosure, CEO Matthew Prince said in a Thursday X post. The network saw thousands of attempts in the 10 hours before the flaws were made public, according to the same post.
PHP developers released emergency patches for both flaws on Wednesday. The same day, the PHP Foundation acknowledged that a shortage of resources had delayed a fix for a critical security flaw first identified in 2024. Fixes have shipped for four supported PHP branches, and the flaws can let attackers run code on vulnerable web servers without logging in. The exploit campaign has been dubbed PHP2Shell.
The vulnerabilities may allow attackers to spread malware or inject malicious scripts into websites. The FBI Cyber Division warned in a Wednesday X post that the flaws could:
"allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks"
FBI Cyber Division
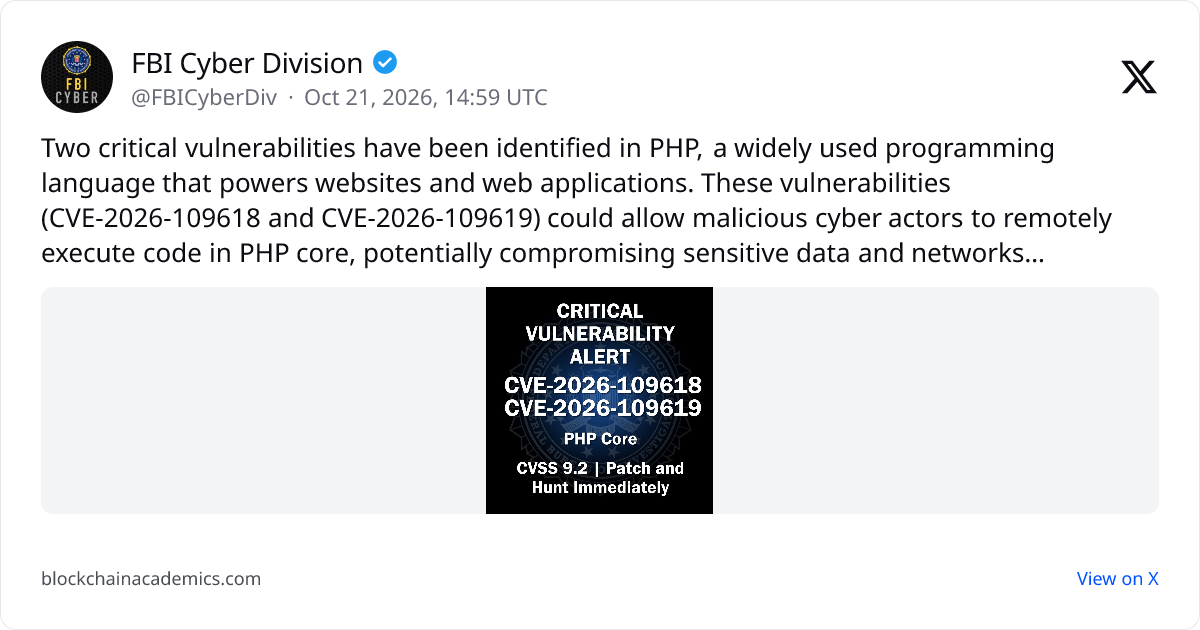
The agency urged organizations to update immediately or take affected systems offline. Multiple organizations and government agencies took websites offline on Wednesday as a precaution.
Scale of exposure
PHP powers an estimated 69% of websites with a known server-side language, according to W3Techs. About one in five websites routes traffic through Cloudflare's network, according to the company. The counts Prince cited cover attempts seen on that network.
Cloudflare, which launched the NetDollar stablecoin for AI payments, is reporting the attack traffic from its position as an infrastructure provider. The PHP Foundation has tied the delay on the 2024 flaw to a lack of resources.
The FBI's guidance for organizations running affected PHP installations is to patch immediately or take systems offline.