Binance Warns iOS Flaw Could Expose Wallet Seed Phrases and Keys
Binance warns an iOS flaw dubbed worse_query could let malicious apps read wallet seed phrases, private keys and logins. Affected version lists differ, and it is unclear whether Apple's latest updates fix it.
Update: November 10, 12:47 UTC
Attackers are reportedly exploiting the "worse_query" flaw through disguised sideloaded apps, such as fake file managers distributed via Telegram, according to Blockonomi's summary of Binance's warning.
Blockonomi did not say whether Binance has tied any of these apps to confirmed wallet thefts.
Original report: November 10, 12:19 UTC
A malicious app on an affected iPhone could read your seed phrase. That is the warning Binance put out on Tuesday, flagging an iOS flaw it says reaches well beyond its own products.
The exchange said seed phrases, private keys and login credentials are "at risk across the entire ecosystem," and called it "an iOS-level issue, not unique to Binance." The warning went out on X.
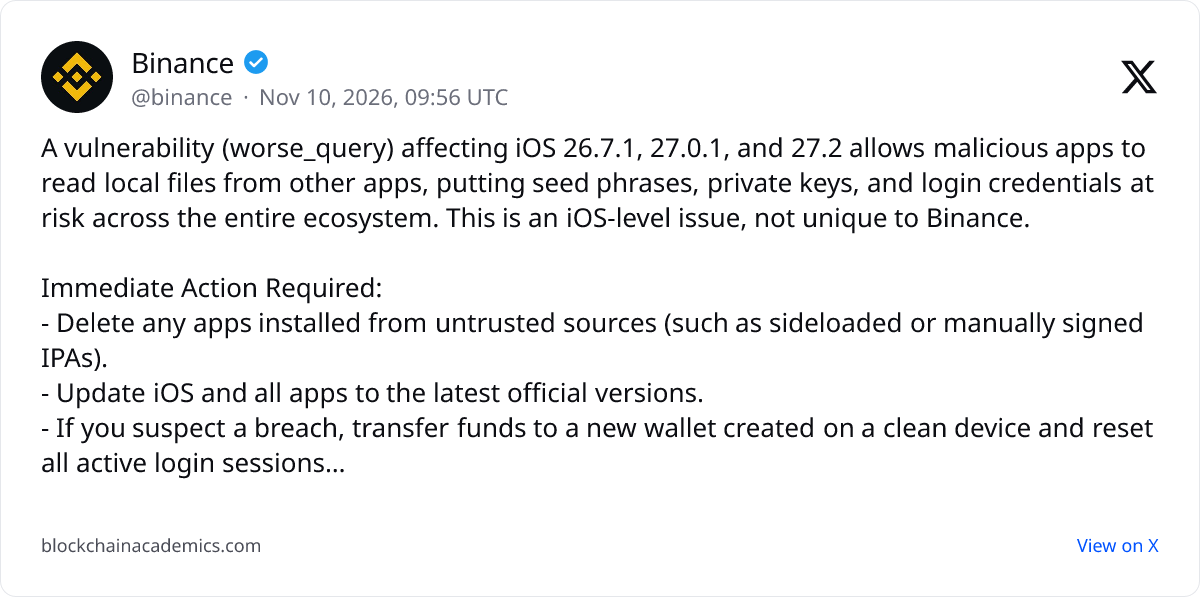
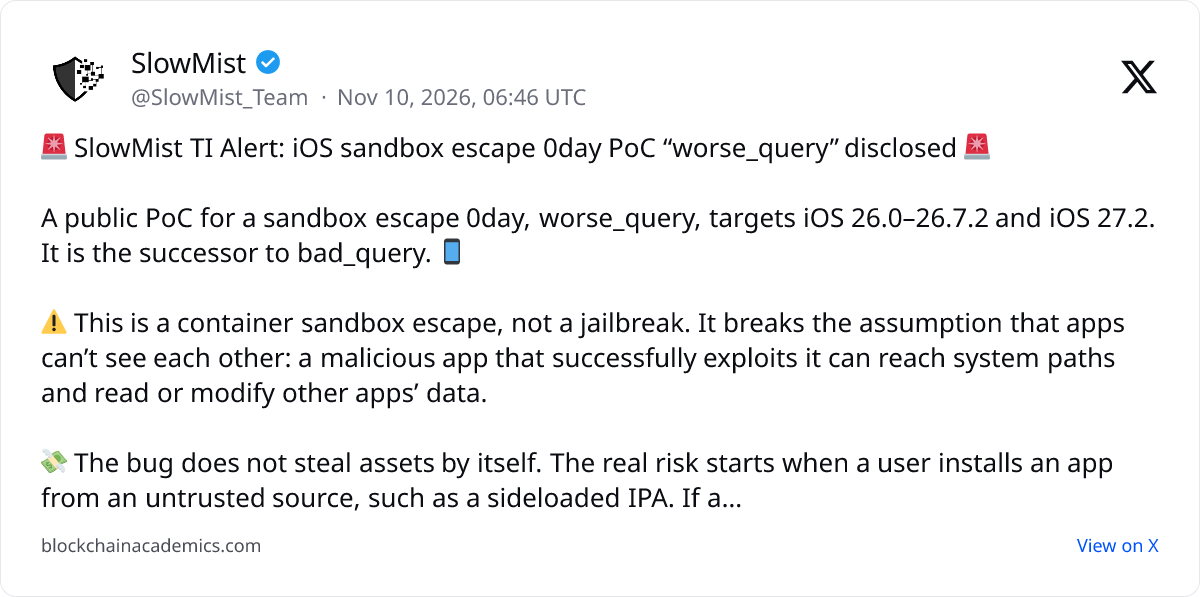
SlowMist flagged the issue earlier the same day, saying a malicious app could read recovery phrases if a wallet stores them unencrypted on the device.
What the flaw does
The bug is called "worse_query," a sandbox escape. iOS normally isolates each app's files from every other app. This flaw lets a malicious app reach into that storage. Researcher forcequitOS disclosed it publicly on Sunday and credited another researcher, 0xjohnny.
Exposure depends on how each wallet stores its secrets. Apps that keep recovery phrases or credentials in accessible local files are the ones carrying real risk. Wallets that encrypt them are in a better spot.
Which iOS versions are affected
The version lists don't line up. Binance listed iOS 26.7.1, 27.0.1 and 27.2 among affected versions. The public GitHub project tracking the flaw lists iOS 26.0 through 26.7.2 and iOS 27.2. Treat both as provisional.
Patch status is murky too. Apple released iOS 27.2.1 and 26.7.3 on Monday, but it is unclear whether either fixes the flaw. Apple's advisories for iOS 27.2 and 26.7.2, released October 26, 2026, do not name worse_query, and a GitHub project reported on November 8 that available releases had not patched it.
What Binance tells users to do
Binance urged users to:
- Delete apps installed from untrusted sources, including manually signed IPA files.
- Update iOS and all apps to the latest official versions.
- Move funds to new wallets created on clean devices if they suspect a breach.
Resetting active login sessions is also on the recommended list.
A Binance spokesperson said the "underlying file-access risk may apply across the iOS ecosystem" and that the exchange has identified no confirmed cases of attackers using this bug to access crypto wallets or steal funds.
Context
The practical risk is narrow but real. An attacker needs a malicious app running on the device, and Binance's advice points squarely at apps from untrusted sources. Still, anyone holding a seed phrase in plain local storage on an iPhone should take this as the nudge to audit where it lives. No confirmed thefts yet is not the same as safe.
This isn't the first iOS-side warning aimed at crypto users. In September, Binance warned about FomoPeek, a third-party app whose versions 1.1 and 1.2 reportedly contained malicious code, and CertiK highlighted the DarkSword exploit framework. Both are separate attack methods. The alert also comes a week after Binance tied its $6.3B hack to a fake job interview.